Splunk

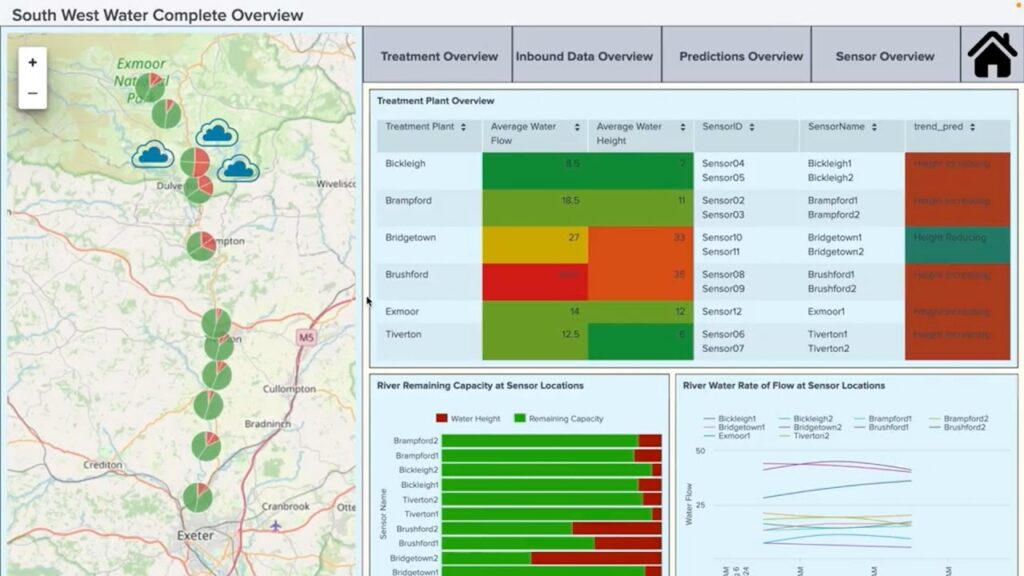
Simulating Real-Time Water Treatment Monitoring with Confluent and Splunk

Video Simulating Real-Time Water Treatment Monitoring with Confluent and Splunk Episode 2 Contact Us Video Summary This demo showcases real-time data streaming from Confluent into Splunk, using simulated water treatment sensor data along the River X. The dashboards provide an overview of treatment plants, river flow, and capacity levels, helping predict and mitigate overflow risks. […]

Simulating Real-Time Water Treatment Monitoring with Confluent and Splunk Read More »
Automated Threat Analysis from Splunk and Somerford

Automated Threat Analysis from Splunk and Somerford

Splunk & Somerford Present: Automated Threat Analysis eBook In an era where cyber threats evolve at an unprecedented rate, the ability to rapidly analyse and respond to potential incidents is critical for maintaining organisational security. Security operations centres (SOCs) face the daunting task of analysing and responding to threats swiftly and effectively in an environment

Automated Threat Analysis from Splunk and Somerford Read More »

7 Splunk Predictions for 2025

7 Splunk Predictions for 2025

Splunk Presents: 7 Predictions for 2025 As we all look ahead to 2025, changes in the way we process and protect data are expected to continue evolving at break-neck speed. How are businesses aiming to stay at the forefront of innovation whilst simultaneously implementing effective threat mitigation strategies? Splunk and Cisco executives have reflected on

7 Splunk Predictions for 2025 Read More »

Resilience Talks LinkedIn Live: Splunk State of O11y 2024

LinkedIn Live Resilience Talks: The State of Observability 2024 Join Splunk’s Stephane Estevez and Rachel Bourne, along with Somerford’s James Astley, as they discuss the latest trends in observability. Watch in full on YouTube: youtube Episode Summary In 2024, simply having an observability practice is a given. Organisations with leading programs create incredible digital experiences,

Resilience Talks LinkedIn Live: Splunk State of O11y 2024 Read More »

Splunk for Security: SSE – Security Searching – Episode 1

Video Splunk for Security: SSE – Security Searching Episode 1 Series Overview Video Summary This video introduces the advanced search assistance features in Splunk Security Essentials, focusing on how they help identify unusual behaviour patterns. The session begins with a demonstration of the “Detect Spikes” feature, which identifies significant increases in activity, such as a

Splunk for Security: SSE – Security Searching – Episode 1 Read More »

Splunk for Security: SSE – Data Inventory – Episode 4

Video Splunk for Security: SSE – Data Inventory Episode 4 Series Overview Video Summary This video provides an in-depth introduction to the data inventory features of Splunk Security Essentials, showcasing how they help organisations manage and categorise their data sources. It begins by demonstrating the data introspection process, which scans your Splunk environment to identify

Splunk for Security: SSE – Data Inventory – Episode 4 Read More »

Splunk for Security: SSE – Security Data Journey – Episode 9

Video Splunk for Security: SSE – Security Data Journey Episode 9 Series Overview Video Summary This video introduces the Splunk Security Data Journey, a framework designed to guide organisations through six maturity stages of security operations using Splunk Security Essentials. Starting with Stage 1: Collection, it emphasises the importance of onboarding high-value data sources to

Splunk for Security: SSE – Security Data Journey – Episode 9 Read More »

Splunk for Security: SSE – Security Content – Episode 8

Video Splunk for Security: SSE – Security Content Episode 8 Series Overview Video Summary This video provides an in-depth look at the security content features within Splunk Security Essentials, showcasing how they help organisations explore and implement tailored use cases for their security needs. Starting from the Security Content page, users can navigate through six

Splunk for Security: SSE – Security Content – Episode 8 Read More »

Splunk for Security: SSE – Data Onboarding – Episode 7

Video Splunk for Security: SSE – Data Onboarding Episode 7 Series Overview Video Summary This video explores the data onboarding documentation features of Splunk Security Essentials, which provide detailed guides to streamline the process of integrating new data sources into Splunk. These guides address both the Splunk-side configurations and the vendor-side setup, ensuring a comprehensive

Splunk for Security: SSE – Data Onboarding – Episode 7 Read More »

Scroll to Top